SIEM Integration Overview
EMET can forward events from the agentic AI tools it monitors to your existing Security Information and Event Management (SIEM) platform. This allows your security operations team to correlate AI activity data with network, endpoint, and application events in the tools they already use.
Why integrate EMET with your SIEM:
- Unified visibility — AI agent activity alongside all other security telemetry
- Correlation — Link AI actions to other security events across your environment
- Existing workflows — Leverage established alert routing, escalation, and incident response playbooks
- Long-term retention — Store AI activity data in your SIEM's retention infrastructure
- Compliance reporting — Include AI activity in existing compliance evidence packages (see Compliance Overview)
As EMET's AI agent integration layer expands to additional platforms beyond Claude Code and GitHub Copilot, all captured events feed the same SIEM pipeline — your integration configuration requires no changes.
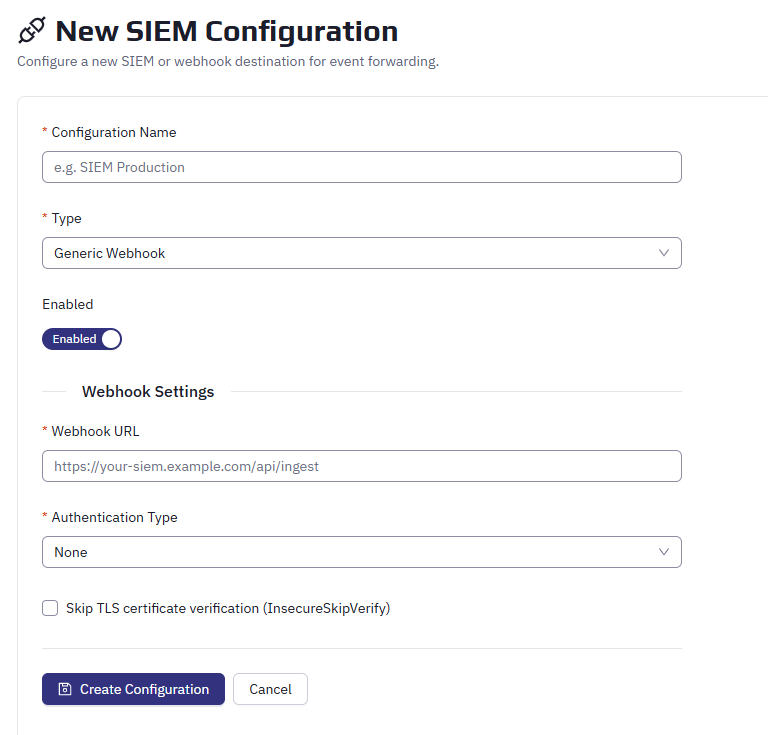
Key architecture properties:
- Asynchronous — Forwarding runs outside the event ingestion path and sends events to your configured destinations
- Transformable — Events are mapped to the native format expected by each SIEM
:::info Available to EMET Customers
The complete SIEM integration documentation — including architecture details, event format specifications, configuration guides, data volume estimation, and per-integration setup instructions — is available within your EMET dashboard.
SIEM integration is available on the Enterprise tier. Pro customers can add SIEM connectivity through the SIEM Connector Pack add-on.
Sign in to your EMET dashboard →
Not yet a customer? Start your free trial →
:::